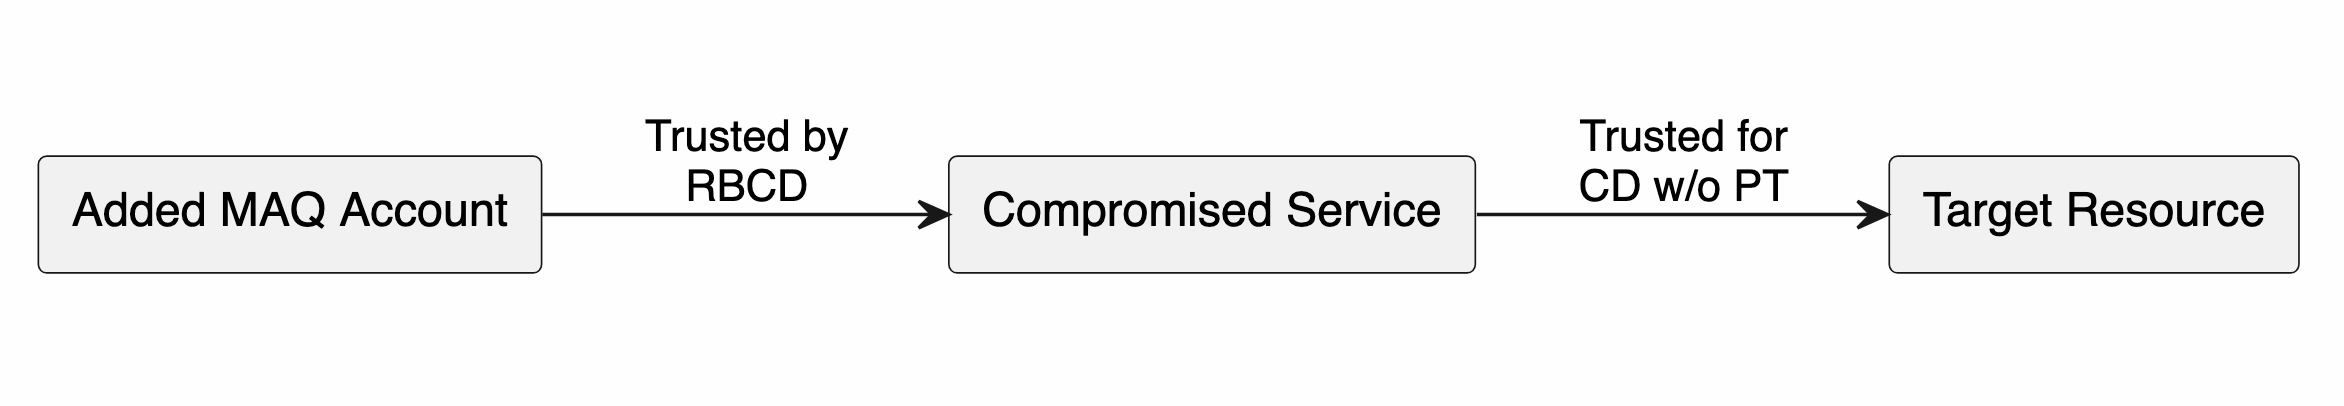
Newly discovered Kerberos delegation abuse path
Security researchers have identified a new Kerberos delegation abuse path that can be exploited to gain unauthorized access to network resources. The flaw allows attackers to trick a service into delegating credentials, enabling them to impersonate users and move laterally within an organization. The discovery highlights the need for tighter configuration and monitoring of Kerberos delegation settings.